

Test and launch your application
Verify ShareAI sign-in, OAuth token handling, model access and customer consent before making a Builder application available.
On this page
Test the complete customer journey#
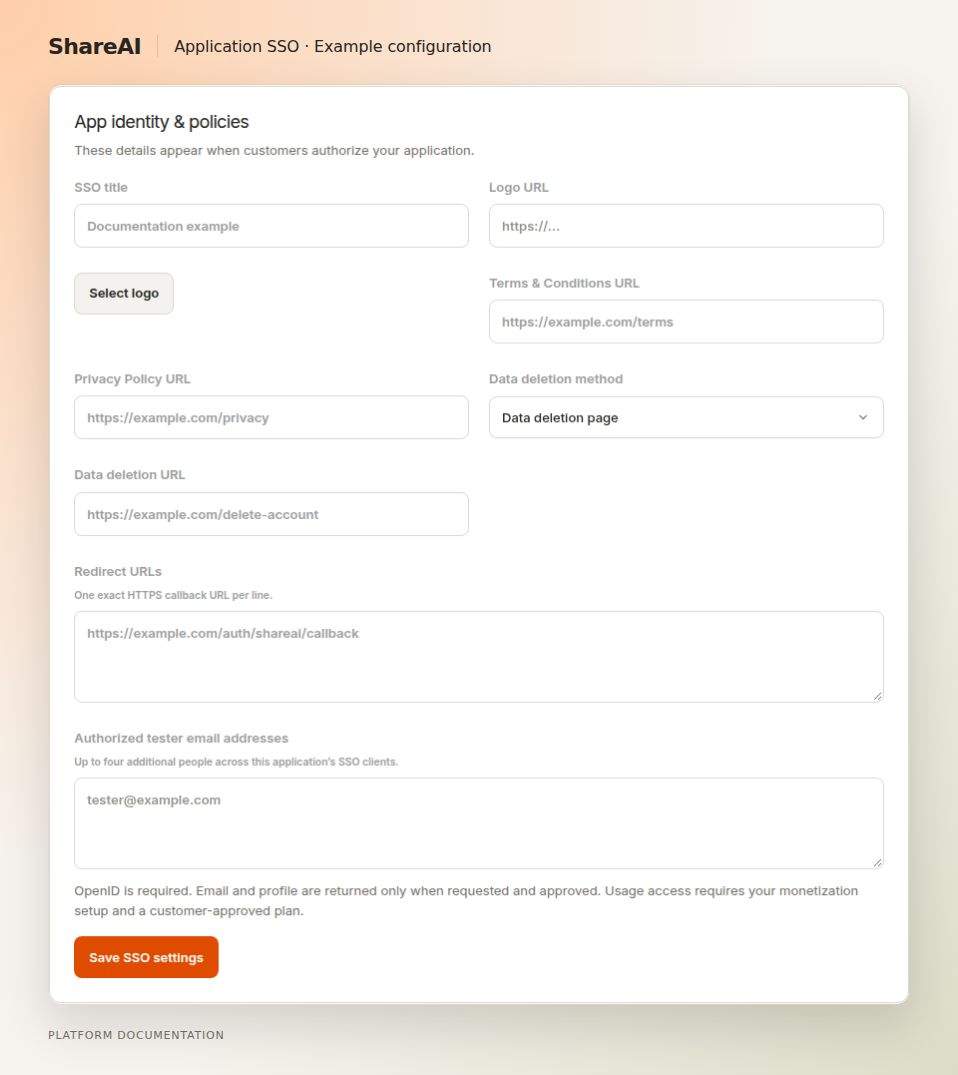
- Start from a signed-out browser and follow the ShareAI authorization redirect.
- Verify the application title, policy links, requested scopes and selected personal or organization account.
- Handle both consent approval and cancellation.
- Complete token exchange on the backend and verify the returned identity.
- Run a small authorized chat request and confirm the usage appears under the intended account.
Test token lifecycle#
Exercise expiry and a single refresh operation, store the replacement refresh token and ensure concurrent app requests do not refresh the same token twice. Test disconnect and reconnect so a customer can withdraw authorization cleanly.
Test operational failures#
- Wrong model or provider access produces an actionable error.
- A 429 response respects Retry-After and has a retry limit.
- A 503 response is presented as temporary unavailability.
- An interrupted stream is marked incomplete.
- A revoked grant leads to reconnect rather than an endless refresh loop.
Review pricing and policies#
Confirm that the consent screen reflects the intended published plan and current application policies. Test organization authorization without assuming the approving administrator’s personal claims will be returned.
Publish through Console#
Complete the application’s current review and publication workflow. Recheck production callback URLs, server-held credentials, allowed users and configured limits. Keep test and production configuration identifiable so a customer cannot be sent to the wrong callback.
Reference#
Last updated September 15, 2026