

Authenticate the Provider API
Enable Provider Remote Access and use a provider UUID and scoped access token for catalog and pricing requests.
On this page
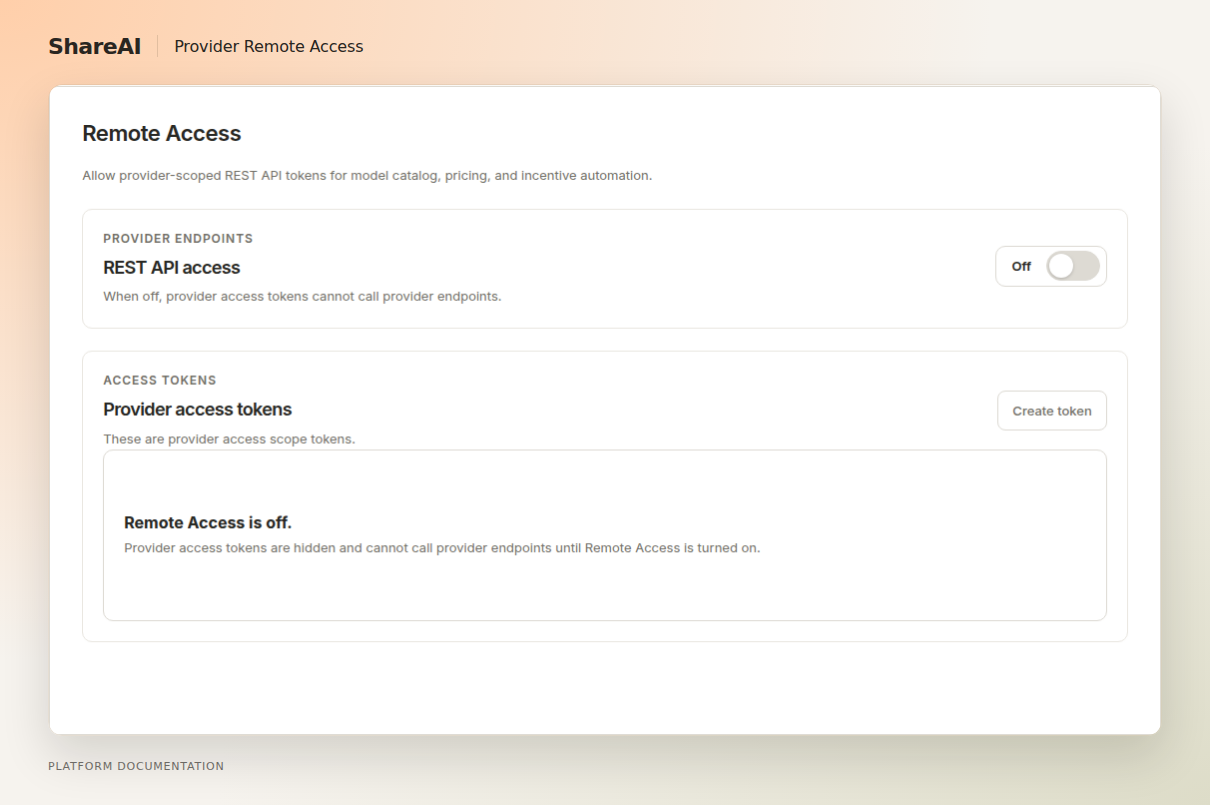
Provider API manages the provider account’s catalog and pricing. Create its credentials in Provider Settings. These credentials are separate from inference API keys and from tokens created for an individual device.
Create access#
- Select the workspace that owns the provider in Console.
- Open the provider’s settings and enable Remote Access.
- Create a named provider access token and save the secret securely.
- Use the provider UUID as the HTTP Basic username and the token as its password.
https://api.shareai.now/api/v1/console/providerVerify provider-level access.
- Base URL
https://api.shareai.now- Authentication
- HTTP Basic: provider UUID and provider access token
- Required scope
provider_models:read
cURL
curl --fail-with-body --request GET \
  "https://api.shareai.now/api/v1/console/provider" \
  -u "$PROVIDER_UUID:$PROVIDER_ACCESS_TOKEN"
Python
import json
import os
import urllib.request
import base64

credentials = os.environ["PROVIDER_UUID"] + ":" + os.environ["PROVIDER_ACCESS_TOKEN"]
headers = {"Authorization": "Basic " + base64.b64encode(credentials.encode()).decode()}
request = urllib.request.Request('https://api.shareai.now/api/v1/console/provider', headers=headers, method='GET')
with urllib.request.urlopen(request, timeout=60) as response:
    print(json.load(response))
TypeScript
const url = "https://api.shareai.now/api/v1/console/provider";
const credentials = `${process.env.PROVIDER_UUID}:${process.env.PROVIDER_ACCESS_TOKEN}`;
const headers: Record = {
  Authorization: `Basic ${Buffer.from(credentials).toString("base64")}`,
};
const response = await fetch(url, { method: "GET", headers });
if (!response.ok) throw new Error(`${response.status}: ${await response.text()}`);
console.log(await response.json());
Named scopes#
| Scope | Permitted operations |
|---|---|
provider_models:read | Read provider summary, catalog, model details and permitted settlement information. |
provider_models:write | Update allowed model pricing and permitted fallback catalog/sharing configuration. |
provider_incentives:write | Change provider incentive settings on their supported route. |
Scopes are checked for the route and HTTP method. The currently issued provider token exposes its configured scopes; a token never grants ownership of a different provider. Keep the enabled state and token status in mind when diagnosing a 403 response.
Device control is another layer#
Starting or stopping a device requires a token created for that device relationship. Enabling Provider Remote Access is a prerequisite, but a provider catalog token alone is not a device-control credential. Continue with Device API authentication.
Revoke access#
Revoke a token when an automation stops needing it. Deleting or revoking one integration’s token lets you retire that integration without replacing unrelated tokens. Turning Remote Access off disables this provider’s remote access path.
Last updated September 15, 2026