

Set up Provider Remote Access
Create and revoke ShareAI provider access tokens and test account-level API access before automating model or pricing changes.
On this page
Use Provider Remote Access for an integration that reads your provider catalog or manages permitted pricing. Start with a read to verify the credential before enabling writes in your integration.
- Select the owning provider workspace.
- Open Provider Settings and enable Remote Access.
- Create a named access token for the integration and record its provider UUID.
- Save the secret securely; do not leave it in a command history or shared document.
- Call
GET /api/v1/providerusing HTTP Basic and verify the returned provider.
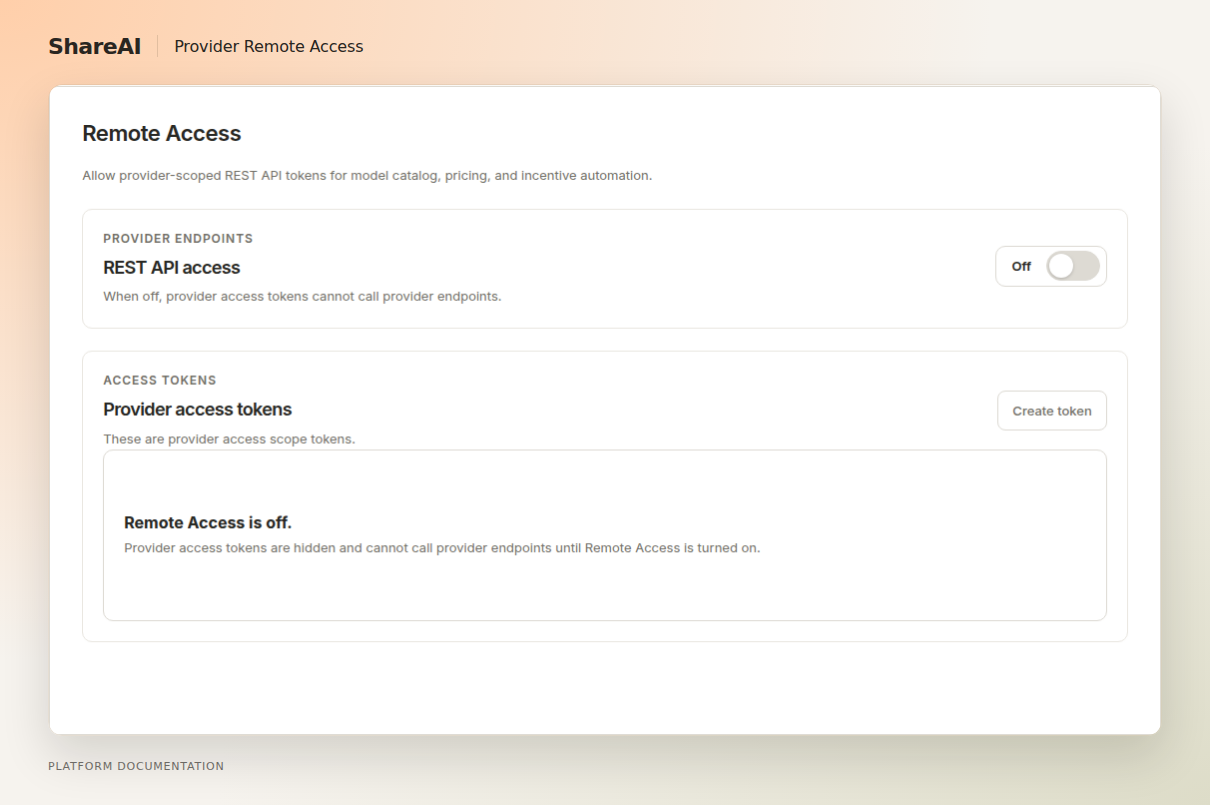
Know the permissions#
Provider tokens carry named scopes such as provider_models:read and provider_models:write. A scope check is tied to the endpoint and method. The API still checks that the authenticated provider owns or can manage the target resource.
Retire an integration#
Revoke its dedicated token when it is no longer needed. If you suspect exposure, revoke promptly and replace the affected secret in the integration. Review the available last-used information instead of sharing the full token with support.
Device commands need device credentials#
Provider Remote Access is a prerequisite for device automation, but provider tokens are not device-control tokens. Open Remote Control for that setup.
Reference#
Last updated September 15, 2026