

Connect your account to a custom application
Understand ShareAI application sign-in, requested permissions, inference consent and how OAuth application access differs from client-work commitments.
On this page
An application can ask you to sign in with ShareAI and optionally authorize inference against a selected account. Read both the application identity and the requested permissions before continuing.
Review an authorization#
- Start from the application you intend to use.
- On the ShareAI authorization page, verify the application identity and policy links.
- Sign in and select the personal or organization account you intend to authorize.
- Review the requested identity permissions and any usage plan or surcharge.
- Approve only the access you intend to grant, or cancel and return to the application.
Identity and spending are different#
Identity-only access lets an application receive the permitted sign-in claims. It does not itself authorize paid inference. The surcharge scope is used for application inference under an accepted usage agreement; openid, profile and email concern identity claims where permitted.
What you pay for#
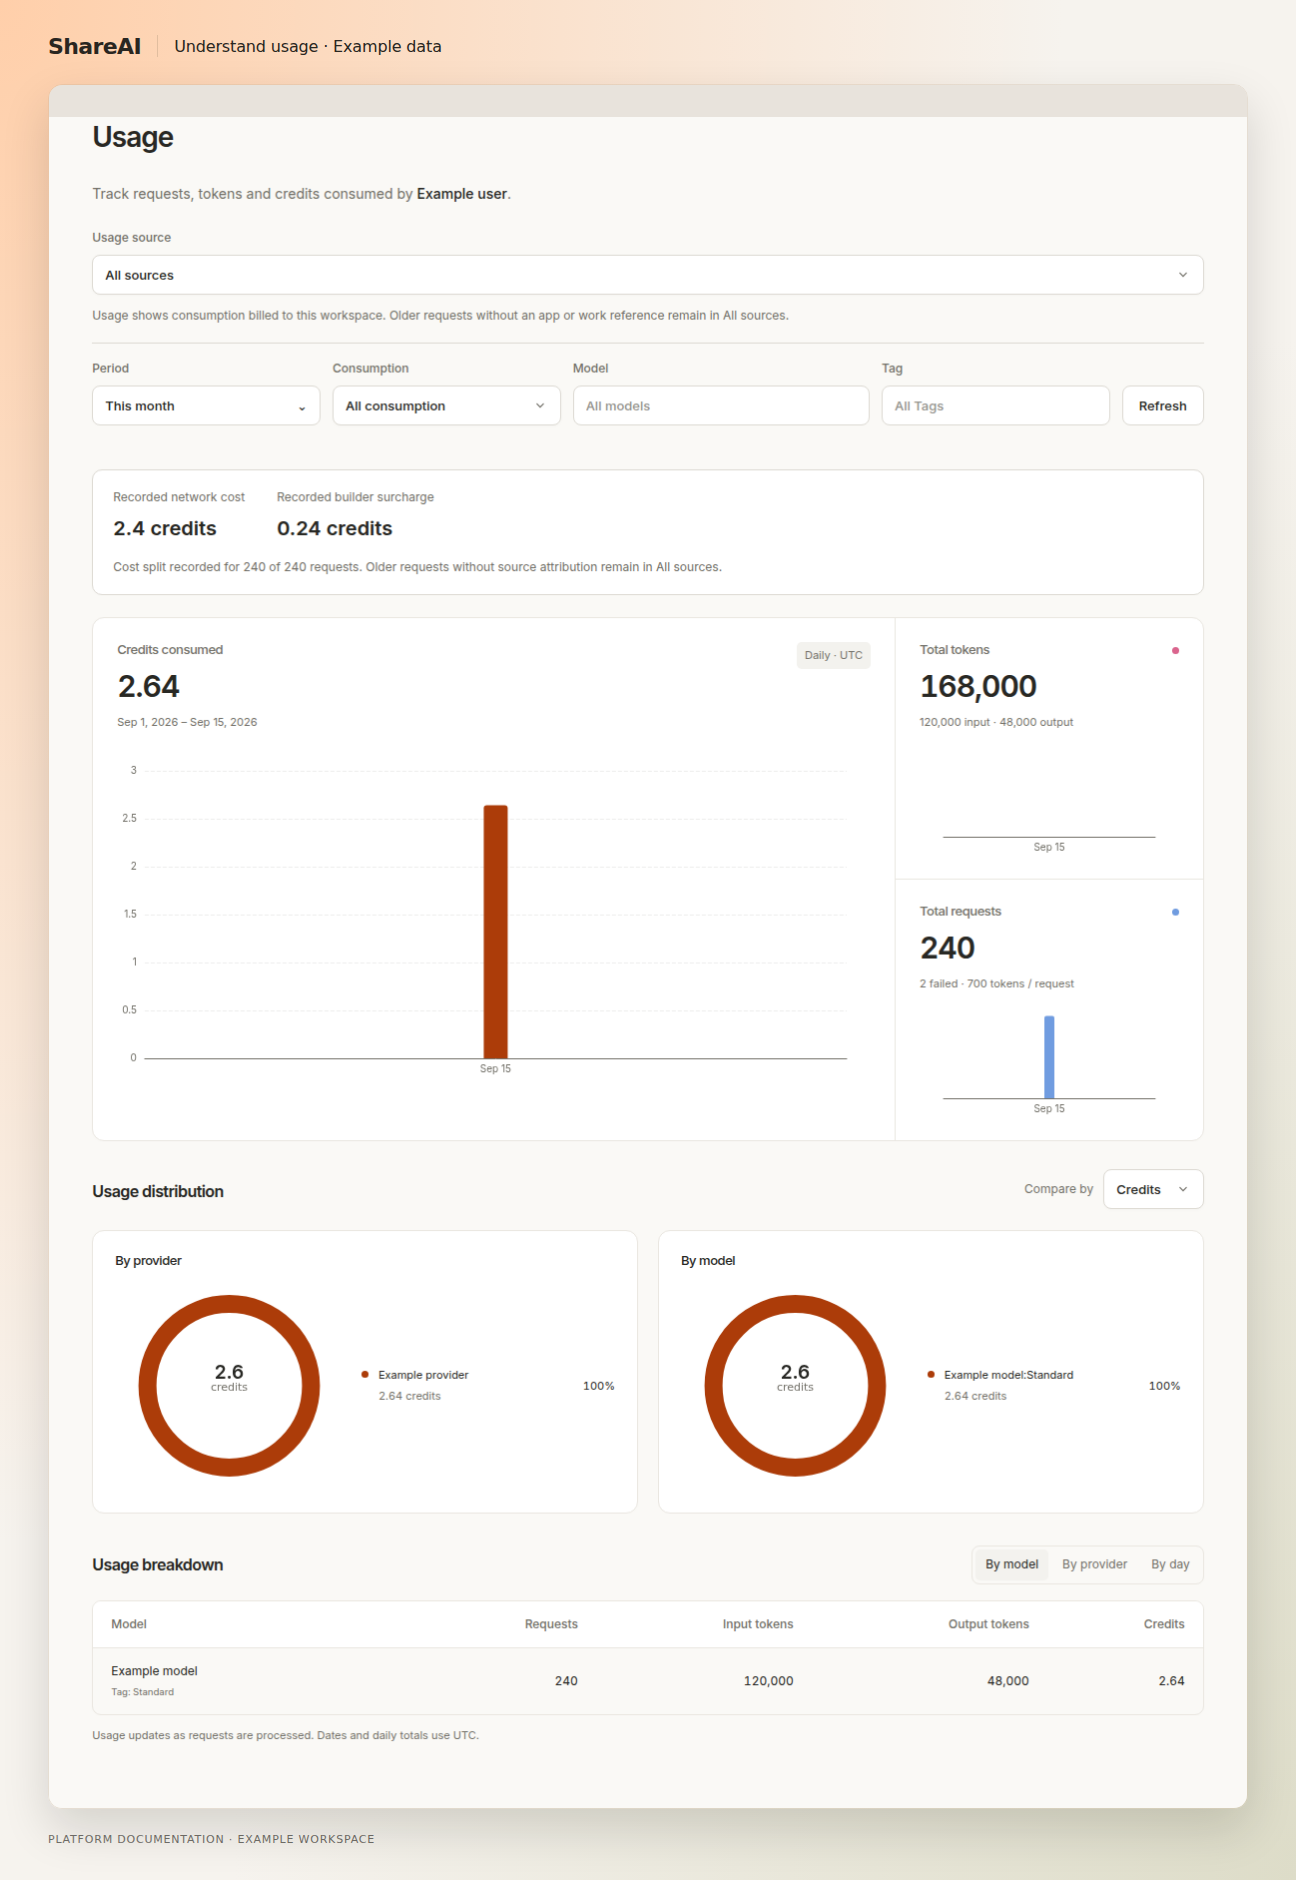
Approved inference uses the selected account under the accepted plan. Review Applications in Usage for recorded activity. Do not assume that switching the active Console workspace transfers an already accepted authorization.
OAuth applications and client work#
Billing → Subscriptions & Commitments currently presents Builder client-work agreements. An OAuth application authorization is a separate flow and should not be treated as the same kind of record. Use the application’s disconnect/account controls or support when you need help ending that connection.
Changes and developer details#
A higher application fee requires new customer approval under the supported managed flow. Developers should follow the Auth guide and accepted billing agreements to implement the lifecycle correctly.
Last updated September 15, 2026