

Restrict an API key to models and providers
Configure ShareAI API key model and provider access, understand combined restrictions and distinguish permission from device-routing priority.
On this page
Access restrictions limit what a key may use. They are useful when an integration should reach only a specific set of models, providers, or both.
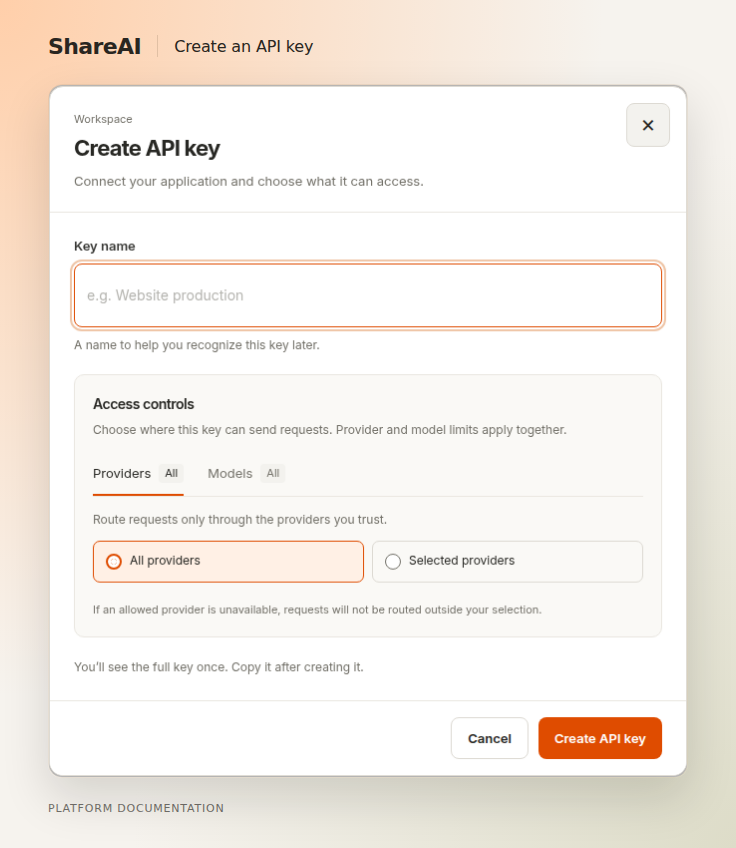
Configure access#
- Open API keys in the owning workspace.
- Open the key’s access configuration.
- Select the allowed models and/or providers exposed by the configuration.
- Review and save the selection.
- Test an allowed request and handle access-denied errors in your application.
| Configuration | Meaning |
|---|---|
| Model restriction only | The request must target an allowed model. |
| Provider restriction only | Execution must use an allowed provider. |
| Both restrictions | Both the model and provider must be allowed. |
| No explicit restriction | The key is not narrowed by that restriction; account permissions and availability still apply. |
Restrictions apply to fallback too#
An alternate route must remain inside the key’s permitted access. A fallback cannot turn a disallowed provider or model into an allowed one.
Priority is separate#
Priority over my Device influences which eligible device is tried first. It does not remove model/provider restrictions or create model availability.
If an expected request is denied#
Compare the exact model identifier, provider restriction, workspace and credential in use. Check that the integration actually loaded the updated key configuration before broadening permissions.
Last updated September 15, 2026